Cyber threats are part of modern warfare: Ukraine shares its wartime experience at Hybrid CoE Course

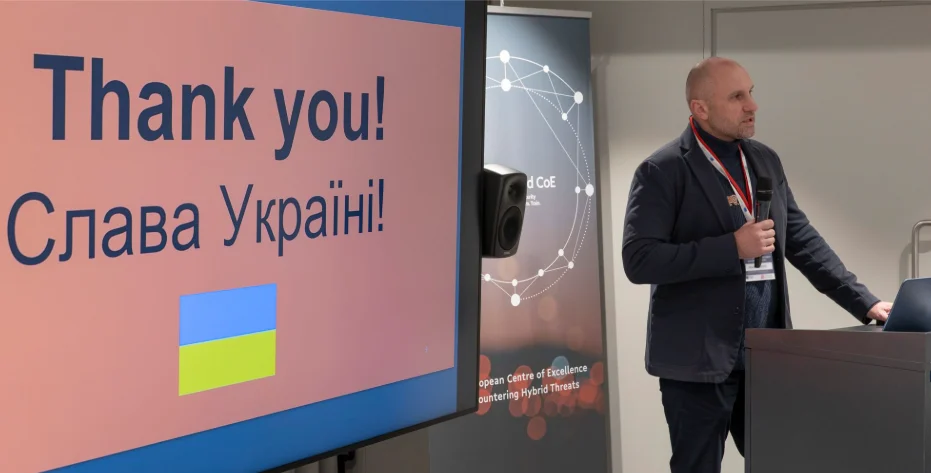
Ukraine’s Ministry of Defence shared practical lessons from countering Russian hybrid operations during a training course run by the European Centre of Excellen
The Ministry was represented by colonel Oleksandr Gain, Director of the Strategic Communications Department. “We wish we had never had to go through this,” he said at the start. “But for us, hybrid cyber warfare is not theory. It’s everyday life.” His presentation covered the scale of the threat, the methods of attack, and two real-world cases.
Scale and trends
Over the past year, hybrid threats with a cyber component have remained very intense. They are also becoming more sophisticated as attackers make use of readily available software and hardware. According to CERT-UA, Ukraine recorded 3137 cyber incidents in the first half of 2026, up 8% from the second half of 2025. These figures include only detected cases, so the real picture is likely much larger.
What makes these attacks hybrid is the combination of massive strikes and targeted operations. The targets are no longer limited to individual workstations. Attackers go after user accounts, mobile devices, information systems, server and DevOps infrastructure, and specialised military systems.
Oleksandr Gain also pointed to another trend: the use of artificial intelligence. It helps the enemy scale up and refine phishing campaigns, build convincing fake websites and generate malicious content.
It starts with one person and ends with the whole system
The Ministry of Defence representative outlined four levels of attack, from the smallest to the largest: the user, the device, the infrastructure and the strategic level. The goal is the same each time: intelligence gathering, influence and harm to society.
- At the user level, phishing and social engineering are used to steal passwords. Against military personnel, fake service-related topics work best: demining, drones, personnel files. Malware can be disguised as a routine update.
- Next comes the device. Malware provides hidden remote access, and a compromised phone gives away its location, contacts, call history and passwords.
- At the infrastructure level, attackers look for vulnerabilities in digital services, servers and DevOps processes. In other words, they break into both the systems themselves and the way those systems are built.
- The strategic level means espionage, and later destruction.
The Nova Post case: one target, two vectors
The first example was Nova Post, Ukraine’s largest delivery service. Russia strikes the company’s terminals and logistics hubs with missiles, as happened with its terminal in Lutsk. At the same time, the company was hit by a DDoS attack on its IT systems. Services had to be temporarily suspended, but the IT team stopped the attack and switched to backup systems.
“This is what hybrid means,” Oleksandr Gain explained. “Physical and digital attacks on the same target.” In both cases the aim was the same: to stop the company from operating.
Why Nova Post? Because it delivers goods and cargo to people and to the front line. It connects people across Ukraine and abroad, including in Poland. Online shops and small businesses depend on it, and when it stops, the whole country’s economy feels it. Formally, the company is not classified as critical infrastructure, but in practice it is. That is exactly why Russia chooses it as a target.
Hidden Shahed relays in Kyiv
The second case concerned Shahed-type drones. “The enemy hides a radio network inside our city to guide drones onto it,” the Ministry representative said.
Russian forces may be using hidden radio transmitters in Kyiv, a so-called MESH network. These allow operators to control drones in real time, even if only for short periods. The drones’ routes run from the north towards Kyiv. In essence, it is a network placed inside the city in order to strike the city itself.
Stopping these relays is very difficult. They make it possible to bypass electronic warfare systems, and operators can adjust a drone’s trajectory right before impact. Estimates suggest that only one to three such devices are operating in the capital, and they switch on for just a few moments during an attack. “A few devices, a few seconds. They are very hard to detect,” Oleksandr Gain concluded.
Ukraine’s experience for European security
The Hybrid CoE course went beyond analysing threats and focused on working out practical responses. During several days of command-post exercises, participants simulated how hybrid operations unfold, assessed response options and weighed the consequences of their decisions.
For European partners, Ukraine’s experience matters especially because it shows how digital attacks can be combined with missile strikes, disruption of logistics, intelligence operations and pressure on the civilian population.
“Cyberspace is not a separate front. It is part of the same war,” the Ministry of Defence representative said in closing.